You can’t secure the castle by reinforcing only the front gate.
SAP can’t be assessed in isolation. We find the invisible ladder — and break it down before an intruder can climb it.
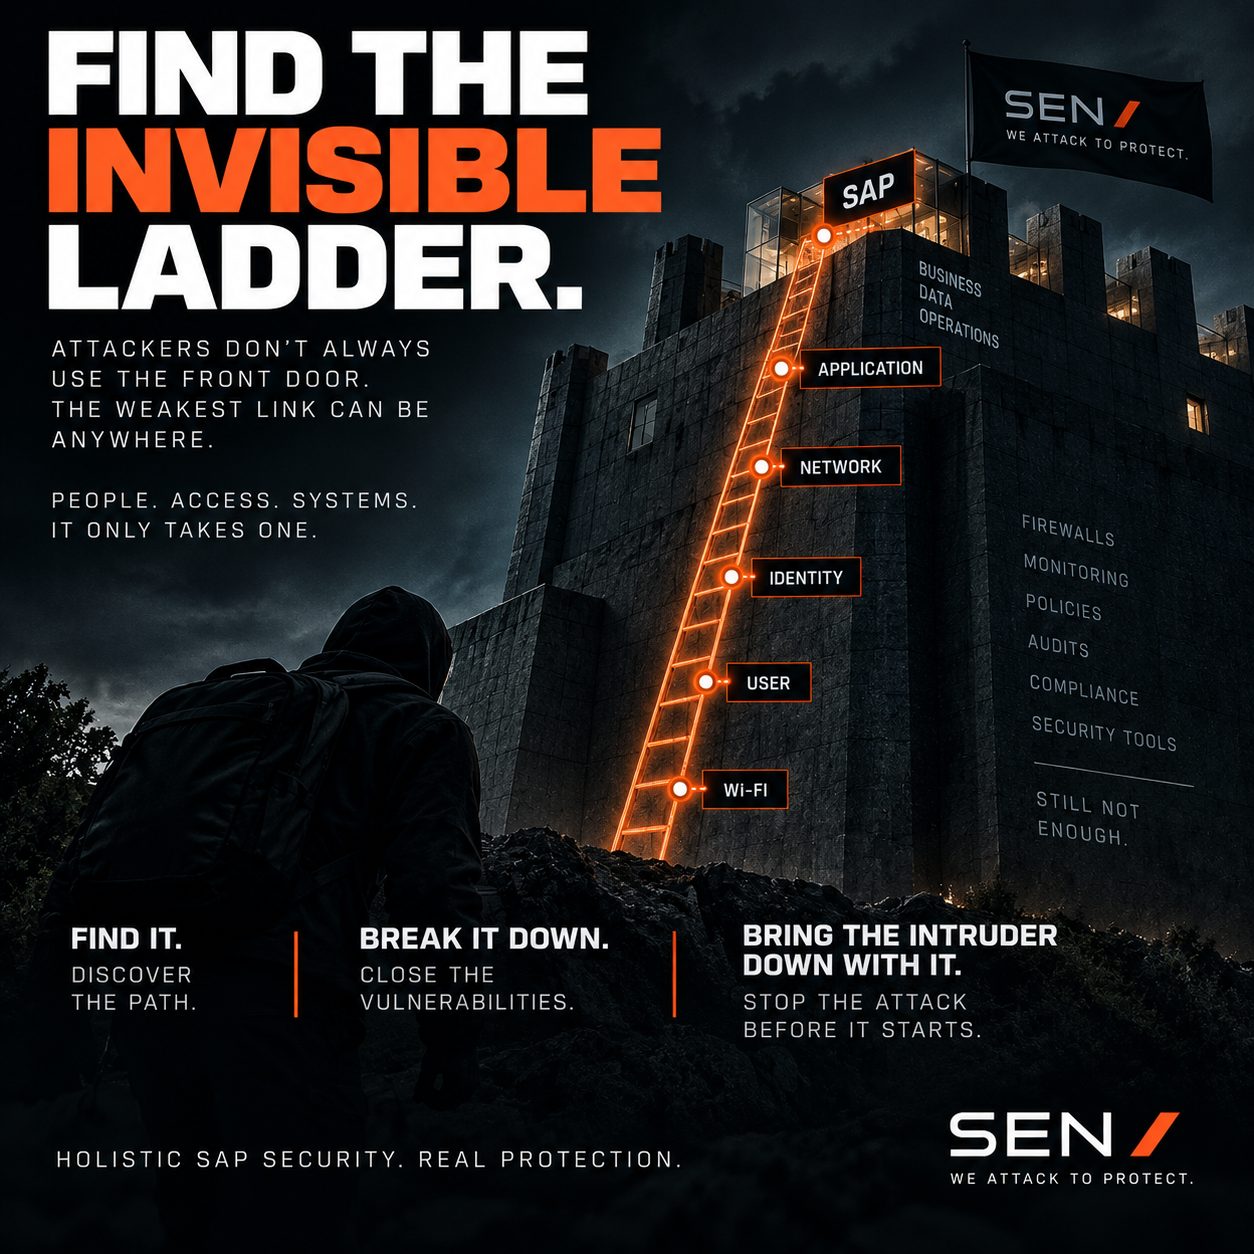
One system. Many doors.
Attack paths move through people, identity, Wi-Fi, network, infrastructure and applications and trusted connections before ever reaching SAP — or they use SAP as the starting point into everything else. Testing SAP alone tells you almost nothing about how a real attacker will actually get to it.
The breach may have started in SAP. The damage rarely stops there. SEN follows it.
Black box. White box. Grey box.
Can your company hear the alarm?
Some SEN tests intentionally generate visible traces — blocked logins or other detectable indicators — so we can test your organization as a defensive system, not just the technology. We watch whether an uninvolved employee, system owner or security function notices, investigates and reports the abnormal activity.
If nobody notices, your security isn’t working.
See this in a real case