Don’t believe us? Good.
You don’t hire SEN to write a report about how someone could hack you. You hire SEN to prove that they can.
No client names are shared. Cases below are anonymized industry examples, presented as supplied.
A badly secured Wi-Fi network was accessible from the parking lot and had a full connection to the internal network. SAP systems were outdated and inadequately maintained. No building access or internal credentials were required to compromise the main SAP environment.
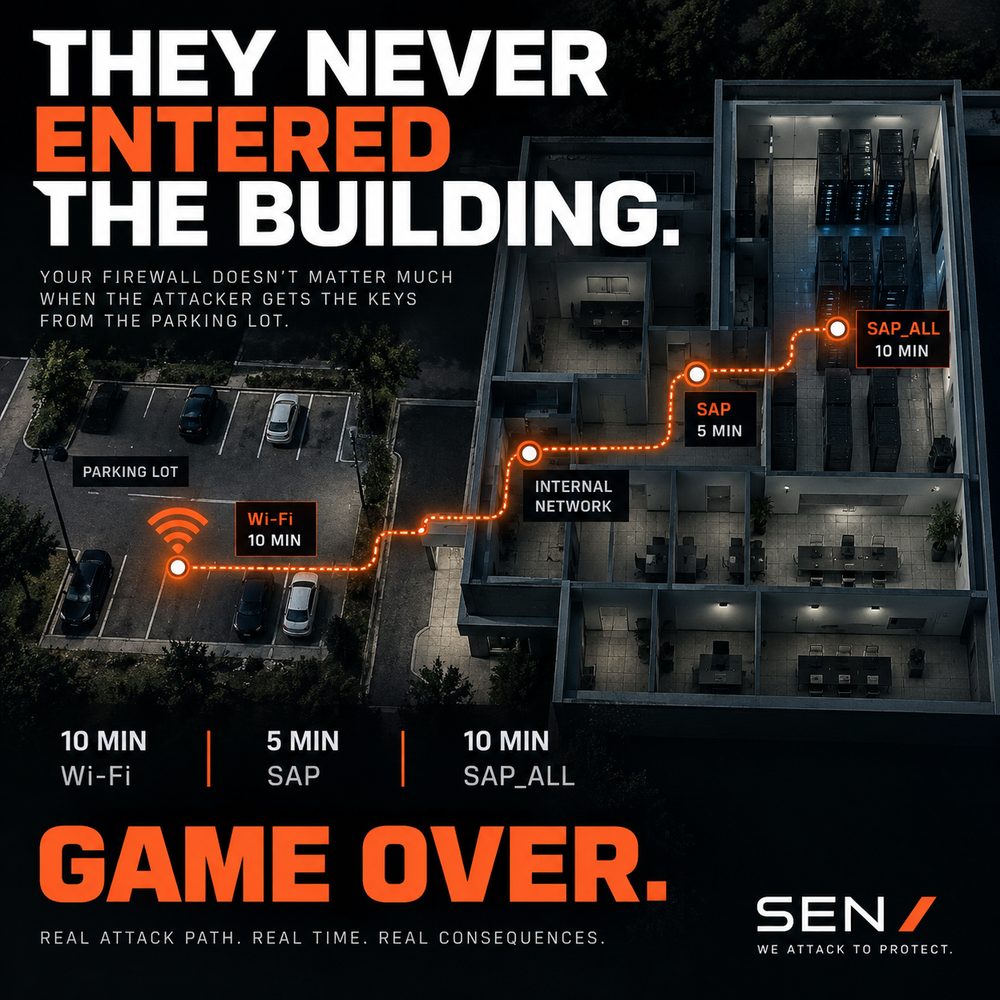
No building access. No internal credentials. Game over.
A customer did not believe there were serious vulnerabilities. SEN had already obtained operating-system access on the test system, adapted the path to production level, and added a privileged backdoor capable of controlling the installed SAP system. When the responsible person challenged the finding, SEN told them to press Enter.
The crucial realization: the connection was to production, not test.
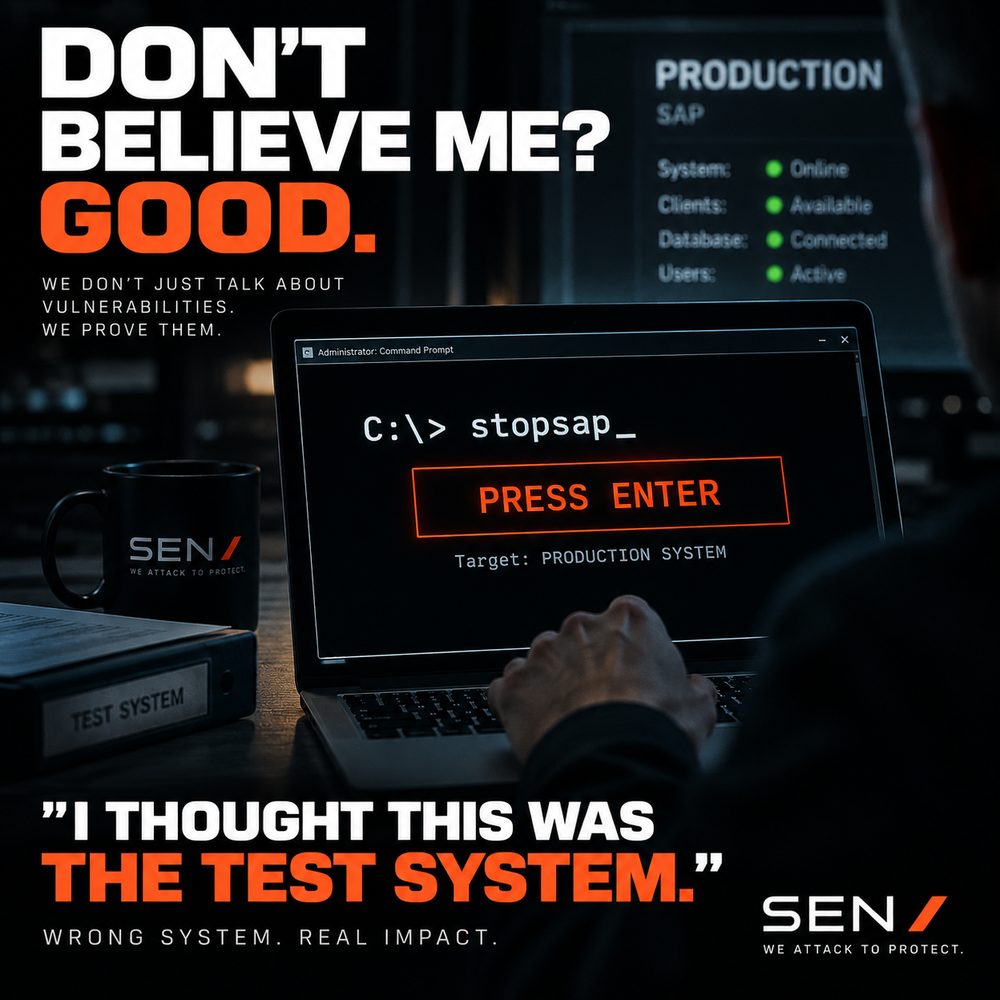
Don’t believe me. Good. Then press Enter.
Some SEN tests intentionally generate visible traces so the organization can be tested as a defensive system, not merely the technology. Activity may create blocked logins or other detectable indicators. SEN then watches whether an uninvolved employee, system owner or security function notices, investigates and reports the abnormal activity.
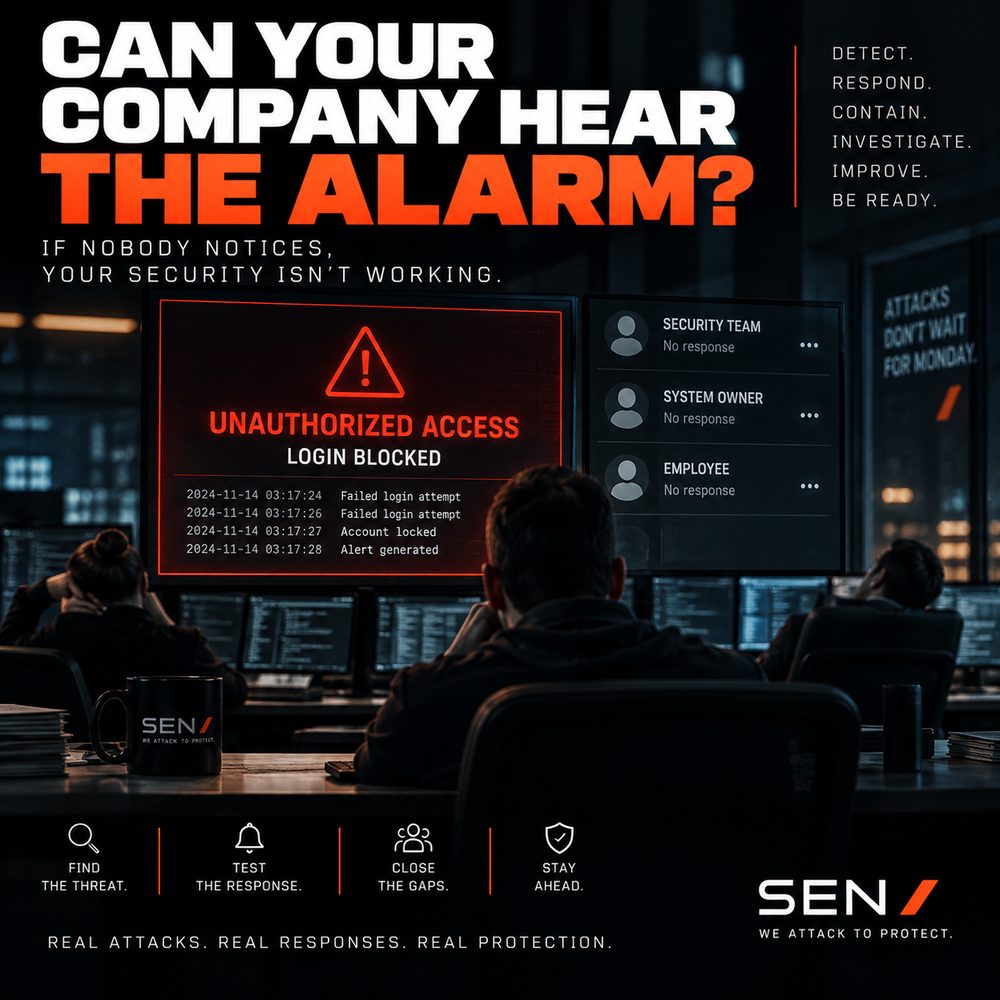
Can your company hear the alarm? If nobody notices, your security isn’t working.
What “zero successful penetrations” actually means
Zero successful penetrations is the standard we hold every engagement to — the goal of repeated attack-and-retest, not a permanent guarantee that a system can never be breached. No provider can promise absolute invulnerability, and we won’t pretend otherwise.