The hacker only needs
to be right once.
You need to be secure
every single time.
SEN finds the one vulnerability that can bring your business down — and closes it. Then attacks again.
You haven’t been hacked.
Yet.
Don’t confuse that with being secure. Two things quietly put businesses at risk — and neither looks like a problem until it is one.
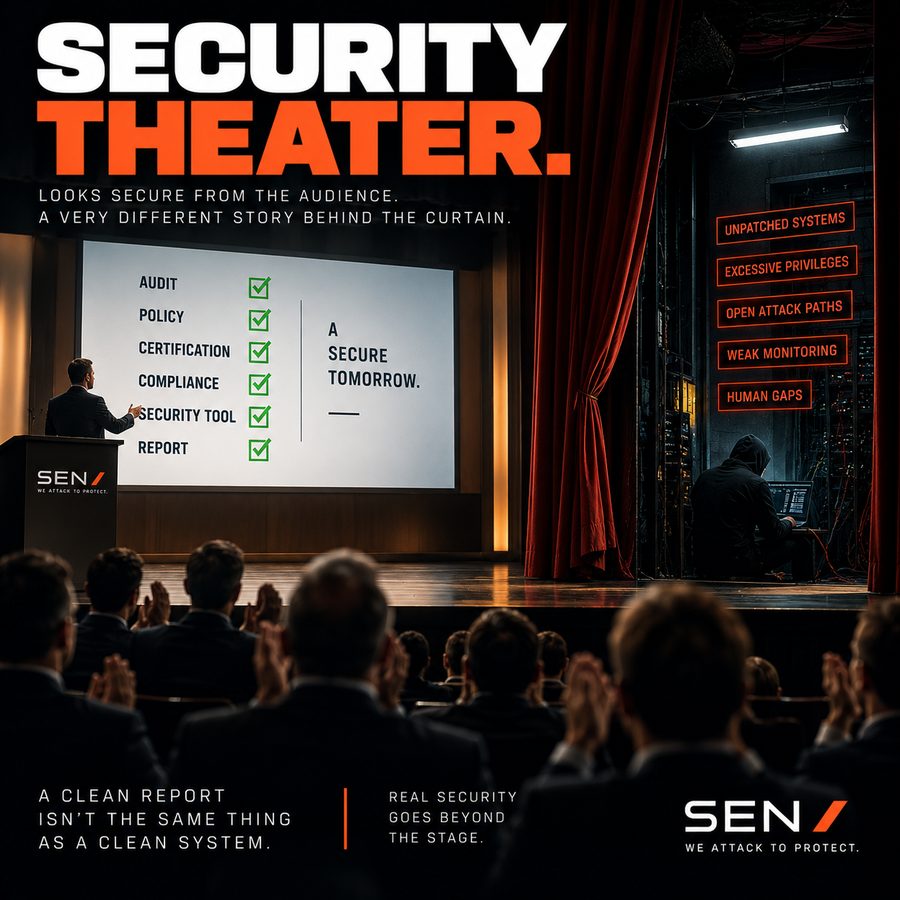
A clean report isn’t the same thing as a clean system.
Passed an audit, bought a product, have the certificates — that’s activity that looks like security. It doesn’t prove resilience under real attack. SEN doesn’t make your security look good. SEN makes sure it holds up when someone attacks it.
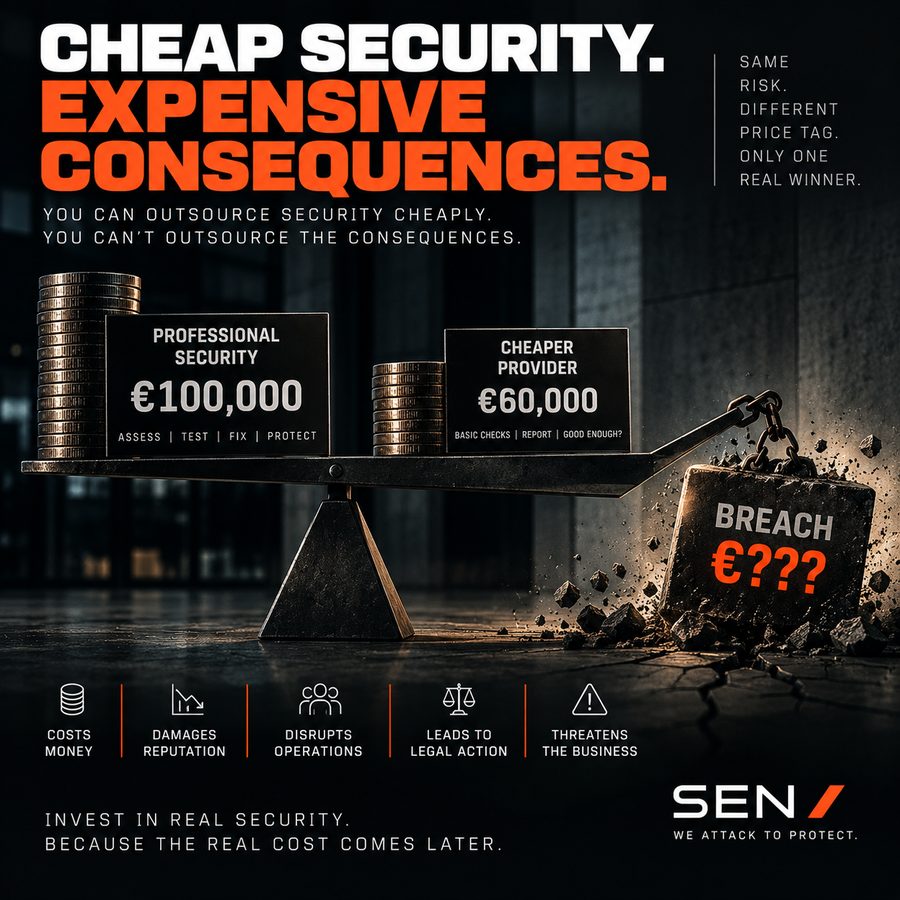
Cheap security. Expensive consequences.
The cheapest security provider can become your most expensive supplier. You can outsource security cheaply. You can’t outsource the consequences. They don’t have to miss ninety-nine vulnerabilities. They only have to miss one.
Before the fire - or after it.
You haven’t been hacked. - Yet.
We attack your SAP environment, find the realistic paths in, and close them — before someone else finds them first.
See ShieldingYou’ve been hacked. Now what?
Containment, scope, root cause, clean environment — and a straight explanation to the people who need one.
See Fire FightingWe attack to protect.
Not satisfied with finding some vulnerabilities. The objective is to find the one that matters, close it, and attack again.
Attack
We go after your SAP environment the way a real adversary would — no scripted checklist.
Expose
Safely embarrass your weak spots. Every real path in, documented.
Fix
Practical remediation guidance, in language your in-house team can act on.
Attack again
Retest. Confirm the fix holds. Establish a clean baseline.
Stay clean
Continued hardening and monitoring support, so the baseline doesn’t erode.
Don’t believe us? Good.
A badly secured Wi-Fi network was reachable from the parking lot, with a full connection to the internal network. No building access. No internal credentials. Game over.
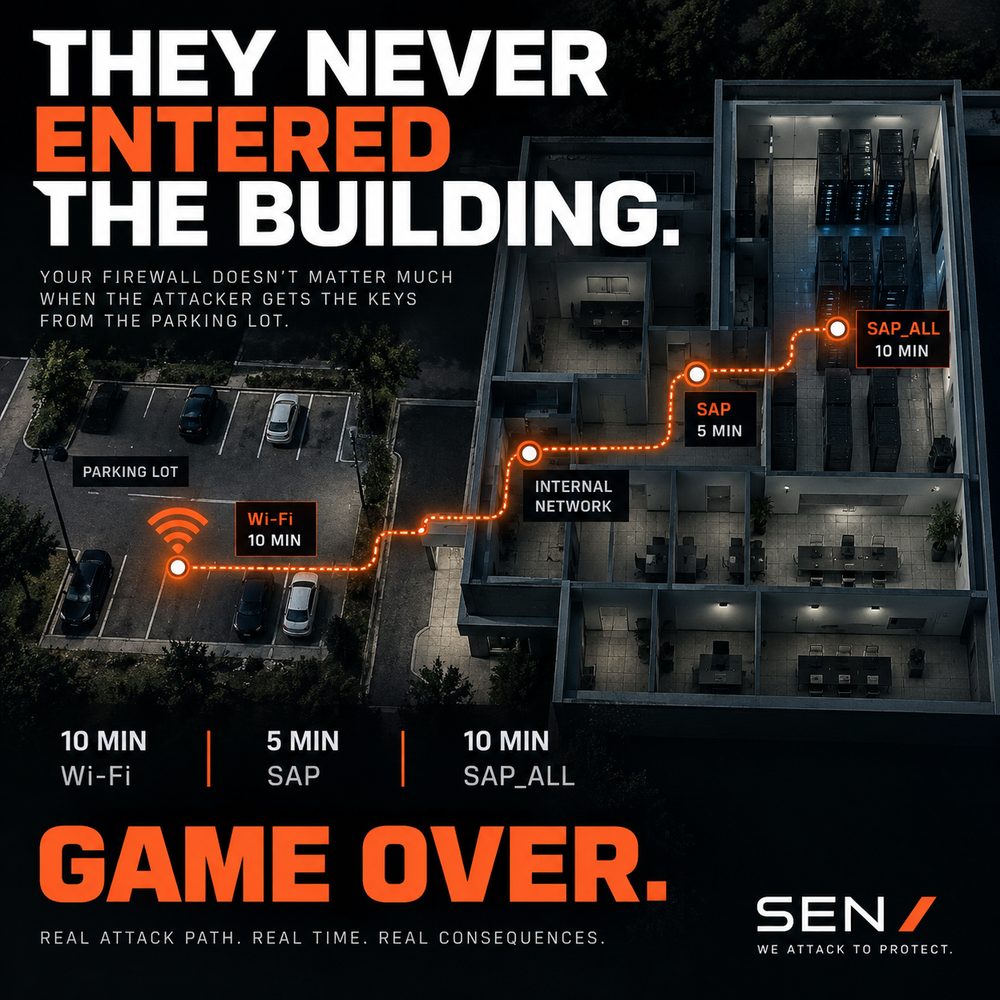
No PowerPoint hacker. No army of juniors.
The person standing in front of you is the person doing the hacking. You don’t hire SEN to write a report about how someone could hack you. You hire SEN to prove that they can.
Find the invisible ladder. Break it down.
SAP can’t be assessed in isolation. Attack paths move through people, identity, Wi-Fi, network, infrastructure and trusted connections before reaching SAP — or use SAP as the way into everything else. You can’t secure the castle by reinforcing only the front gate.
How SEN attacksThe “we haven’t been hacked yet” checklist.
A practical attacker’s checklist for IT teams who’d rather find the holes themselves.