FIELD MANUAL
The “we haven’t been hacked yet” checklist.
How to break your own SAP environment. A practical attacker’s checklist for IT teams who’d rather find the holes themselves.
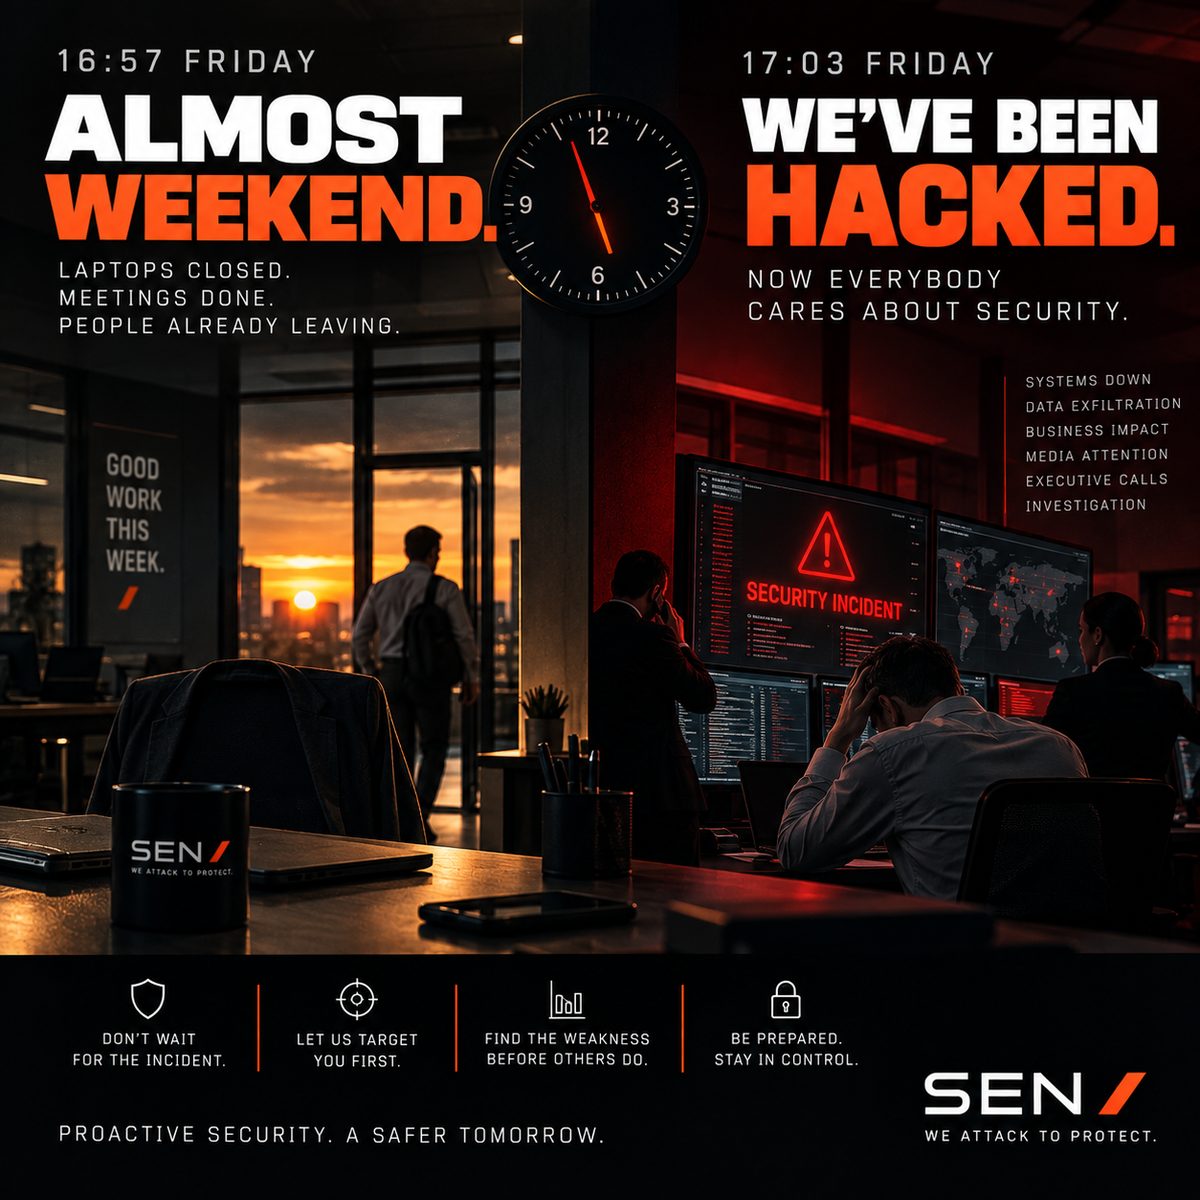
Hire somebody to target you before you find out on a Friday afternoon, when it’s too late. This checklist is how your own team gets there first.
WHAT’S INSIDE
Not a whitepaper. A checklist.
- Where SAP environments are most commonly exposed — Wi-Fi, permissions, outdated systems
- The realistic attack paths that connect people, identity and infrastructure to SAP
- A self-test checklist for your own team to run before an attacker runs it for you
- Anonymized examples from real engagements
MORE FROM SEN
For teams who want the deeper version.
FridayThe “hire someone to target you before Friday afternoon” scenario
NoiseThe full Make Noise case — testing detection, not just prevention
LadderThe invisible-ladder methodology, explained in full
CasesDetailed, anonymized case studies beyond the homepage teasers